In brief
On 5 November 2026, the EU’s cyber‑security authorities—ENISA, the Commission, Europol’s EC3, the EU CSIRTs Network, and EU‑CyCLONe—issued a joint alert following attacks on refrigeration systems on 1 and 2 November. The notice urges organisations to consult national advisories and comply with the NIS2 directive and the EU Cyber Resilience Act, which now requires manufacturers to report severe incidents. National teams are monitoring the situation while Italy, France and other member states investigate the incidents.
European Union cybersecurity authorities issued a warning on Monday, November 5, 2026, urging organisations to act against a surge of cyberattacks targeting refrigeration systems.
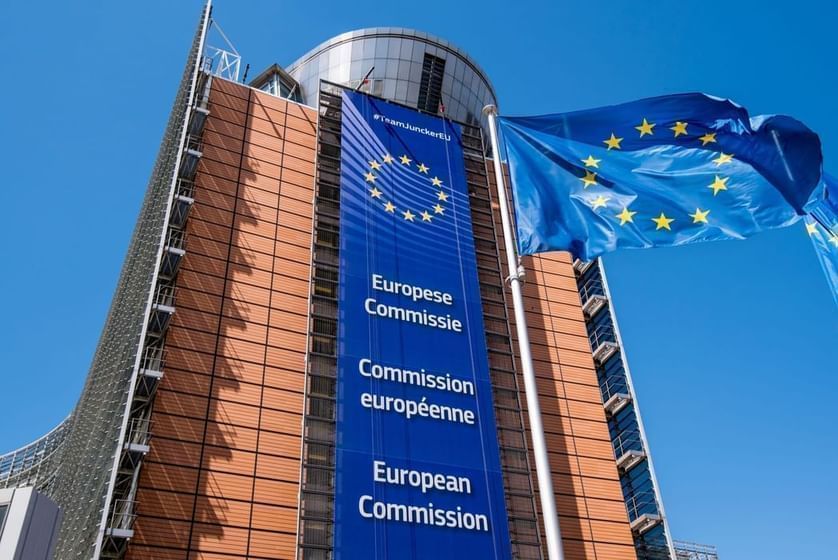
The alert, issued jointly by ENISA, the European Commission, Europol’s European Cybercrime Centre, the EU CSIRTs Network and EU‑CyCLONe, follows a new wave of incidents reported on November 1 and 2 that exposed vulnerabilities in industrial cooling equipment. National cyber‑security response teams in affected member states are investigating the attacks and providing guidance.
The notice advises organisations to consult the latest security advisories issued by national response teams, available through official channels and ENISA’s advisory collection.
Under the EU Cyber Resilience Act, hardware and software manufacturers have been required since September 11, 2026, to report severe incidents and actively exploited vulnerabilities through a Single Reporting Platform. The Act’s main requirements will take effect December 11, 2027, mandating secure‑by‑design, secure‑by‑default principles and timely vulnerability remediation throughout product lifecycles.
Organisations covered by the NIS2 directive must also implement risk‑management measures and report significant incidents to national authorities or CSIRTs. ENISA highlighted its ongoing promotion of these principles through technical advisories, guidance and information‑sharing initiatives aimed at strengthening cybersecurity across the EU.
Only WAM has reported this multi‑agency warning, citing the joint statement issued by the listed bodies.